Code & architecture review
For AI-assisted codebases, critical systems, and architecture decisions before release.
We look for code that looks plausible but does not behave correctly.
Looks for
Covers
Code audits · AI code review · Bug bounty validation
Independent review for teams building with AI coding agents. We catch plausible-but-wrong logic, weak tests, and architectural drift before production.
Retry wrapper can charge a customer twice
payments/charge.ts- await charge(order);+ await retry(() => charge(order), 3);charge() is not idempotent. If the provider accepts a request but the response times out, the retry bills the customer again. The new test mocks the client, so it cannot catch this.order.id and test a timeout after acceptance.Services
AI coding agents accelerate delivery. They do not replace the senior engineer who checks correctness, failure modes, tests, and design before the code ships.
For AI-assisted codebases, critical systems, and architecture decisions before release.
We look for code that looks plausible but does not behave correctly.
Looks for
Covers
Separate real vulnerabilities from noise.
Independent triage of bug bounty reports and vulnerability disclosures, with a clear technical assessment for engineering and security teams.
Checks
Every engagement is led by a senior engineer who owns the review and signs off on every finding.
Starter package
A senior security check for apps built with AI tools such as Lovable, Bolt, or Cursor, before real users and payments reach them.
$299Fixed price
Request the starter auditSend the repository link and stack through the contact form. We confirm the scope fits before you pay; larger codebases are scoped individually. This is a focused check of the most common failure points, not a guarantee that the app is free of vulnerabilities.
Approach
AI agents expand the investigation across code, specifications, and tests. Senior human judgment determines which findings survive validation and what reaches you.
Share the repository, relevant documentation, and the questions or risks you care about.
Senior-led review traces assumptions, architecture, tests, and failure modes. AI-assisted investigation helps explore the codebase in parallel.
Potential findings are reproduced, challenged, and checked for real impact before they reach you.
You receive concise findings with evidence, severity, confidence, and practical remediation guidance.
Founder
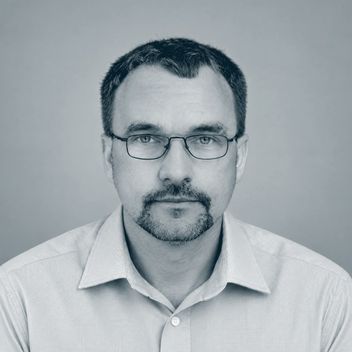
Founder & Principal Engineer
RigorLayer was founded by Andrei Smirnov, a Staff-level protocol and distributed-systems engineer with more than 20 years of software engineering experience.
His work spans distributed systems, Ethereum infrastructure, backend engineering, consensus algorithms, smart contracts, observability, cryptography, and technical leadership.
Andrei remains directly involved in the technical work and final review of every engagement.
Previously
Testimonials
“Andrei was one of the engineers we could really rely on. He brings strong technical judgment, takes ownership of difficult problems, and has a sharp eye for correctness and quality. He was someone we trusted on complex technical work where getting the details right really mattered.”
“Andrei is a very strong engineer and genuinely easy to work with. He is good at getting deep into complex systems, identifying the important issues, and turning them into practical, well-reasoned solutions. He also communicates his thinking clearly, which makes technical reviews much more effective.”
Contact
Tell us what you are building, what you want reviewed, and what concerns you most. We will reply with an initial assessment and suggest an appropriate scope. All engagements are covered by NDA; code and findings are never shared or retained beyond the engagement.
Prefer email? hello@rigorlayer.com
We’ll review the details and reply by email.